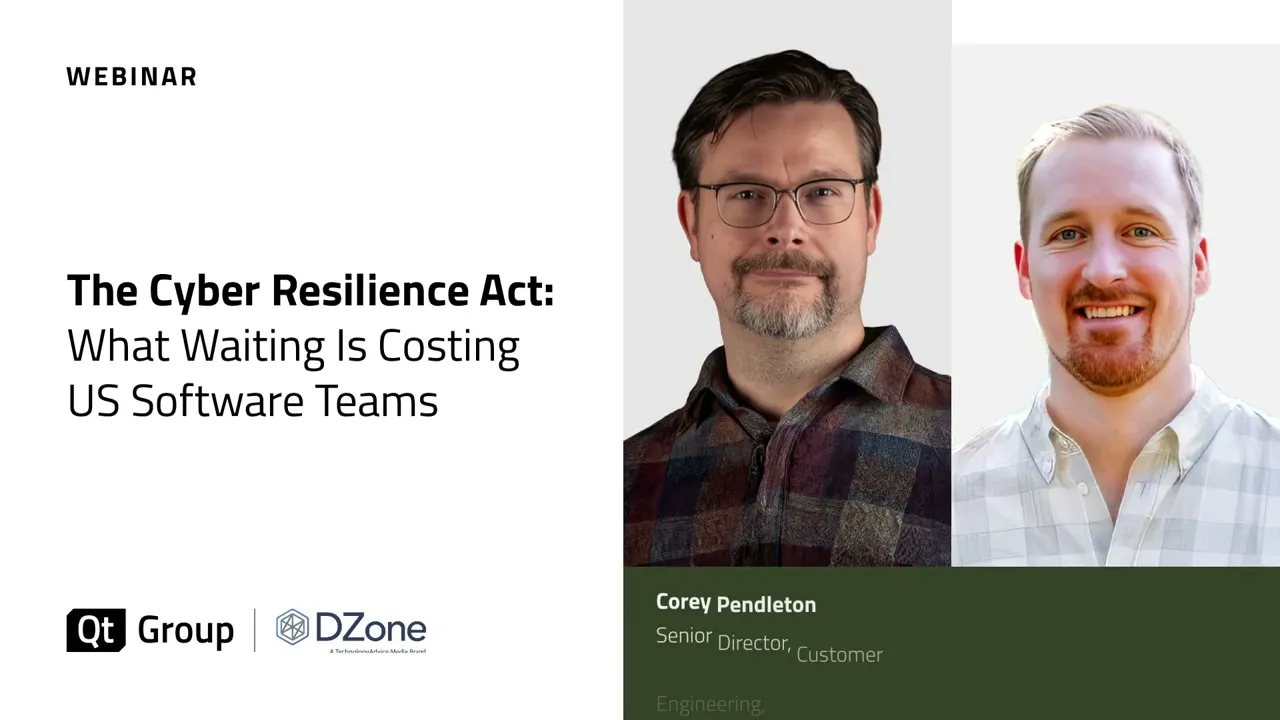
Webinar: The Cyber Resilience Act: What Waiting is Costing US Software Teams
Starting September 11, 2026, the EU Cyber Resilience Act (CRA) requires companies to report actively exploited vulnerabilities and severe security incidents within 24 hours, with full compliance and CE-marking requirements following in December 2027.
This session breaks down what the reporting requirement actually demands, and what counts as an ‘actively exploited vulnerability’ or ‘severe incident’. It also pinpoints what most engineering and product teams are still missing: real visibility into their software's vulnerabilities and dependencies (SBOM), proof of test coverage, and safety-by-design foundations that hold up under regulatory scrutiny.
Oh, here is more
Video: The Making of The Outpace Project
Project Outpace – Qt's Reference Panoramic 3D Automotive Cockpit. Don't Choose Between The Design Yo...
Watch Video
On-Demand Webinar: CI/CD and Continuous Compliance of Embedded Software for Aerospace and Defense
Today, CI/CD for pure software products is well understood. But hardware dependencies and embedded d...
Watch Video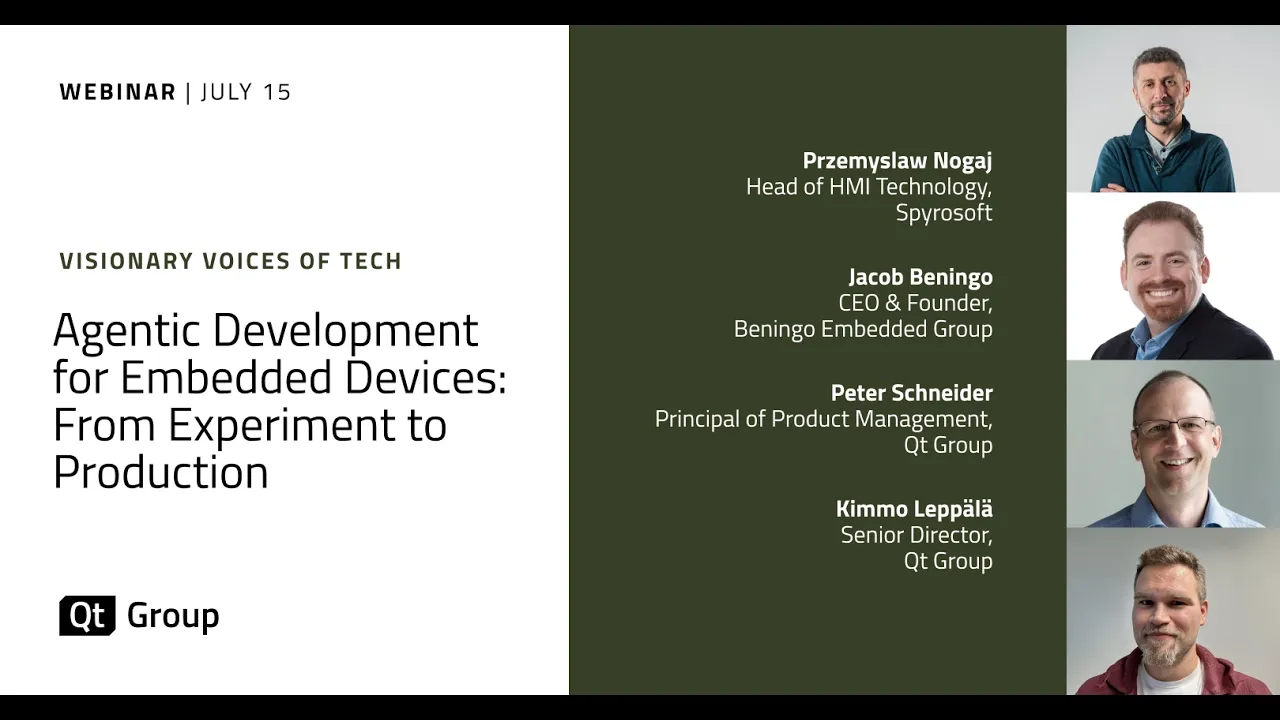
On-Demand Webinar: Agentic Development for Embedded Devices: From Experiment to Production
Agentic development for embedded devices is moving from experiment to production, and regulated indu...
Watch Video