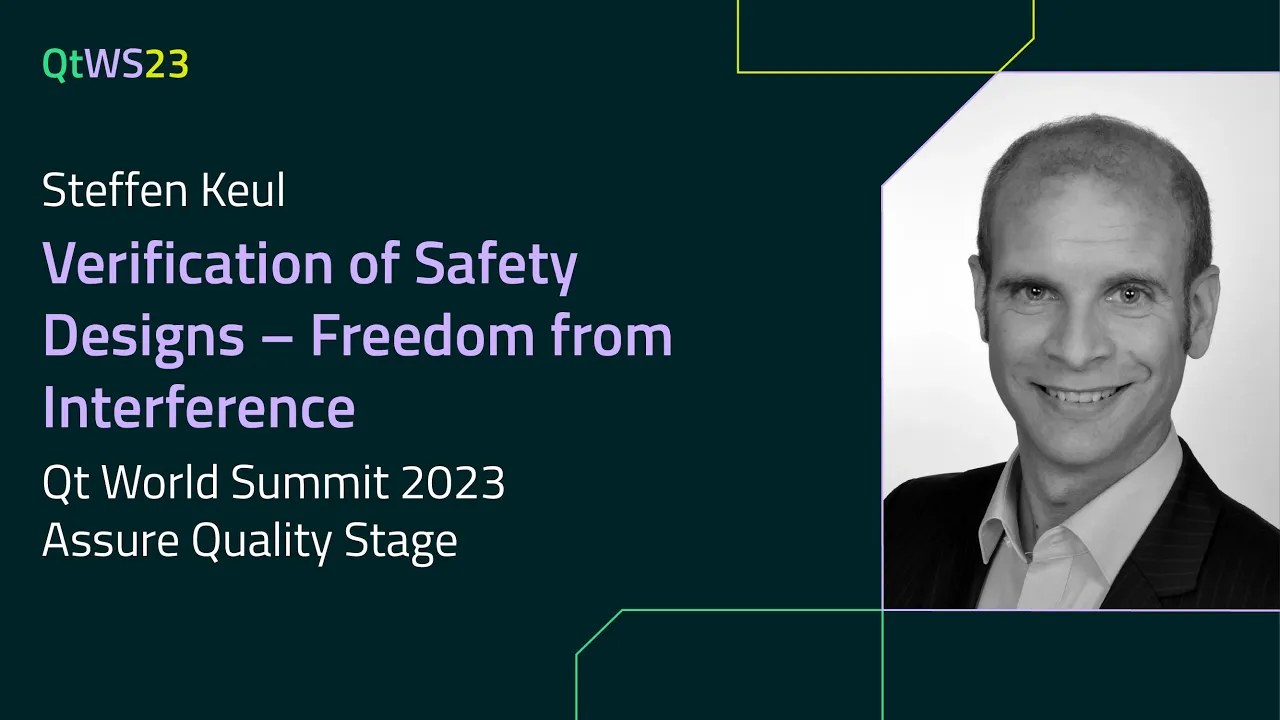
Verification of Safety Designs – Freedom from Interference with Steffen Keul | #QtWS23
Abstract: Safe operation of any embedded device is enabled by a rigorous architectural design. In ISO26262 mixed-ASIL systems, the architecture needs to ensure freedom from interference among the safety-related partitions and between safety-related and QM partitions. After a safety architecture has been defined and verified, static analysis can (and should) be used to demonstrate compliance between implemented source code and this architecture. This presentation highlights one way to apply an architecture check for the aspect of freedom from interference.
About the Speaker: Steffen Keul studied Software Engineering at the University of Stuttgart and gained experience with static analysis during his post-graduate research on static analysis of concurrent systems. For four years, he worked in product management and pre-development of automotive basic software with a focus on functional safety according to ISO26262. In 2017, he joined Axivion's Solution Engineering team. In this role, he strives to find the perfect static code analysis solution for every customer project. Litteraatti
Oh, here is more
Webinar: The Cyber Resilience Act: What Waiting is Costing US Software Teams
Starting September 11, 2026, the EU Cyber Resilience Act (CRA) requires companies to report actively...
Watch Video
Webinar: Architecture-Guided Migration to Rust
Rust promises memory safety and modern tooling — but migrating a large, safety-critical C or C++ cod...
Watch Video
On-Demand Webinar: CI/CD and Continuous Compliance of Embedded Software for Aerospace and Defense
Today, CI/CD for pure software products is well understood. But hardware dependencies and embedded d...
Watch Video
De-Risking AI Playbooks: How to Build Visual UI Tests That Remain 100% Deterministic
Pixel-by-pixel UI testing is too brittle for modern release cycles, yet LLMs introduce a dangerous l...
Watch Video