QtFramework-EasierCRACompliance-Hero-1300x900

CYBER RESILIENCE ACT: THE LIABILITY IS NOW ON YOU

Significantly Reduce Your CRA-Related Efforts and Risks

The EU Cyber Resilience Act (CRA) makes manufacturers liable for their products throughout the lifecycle, including used 3rd party components.

We can help you assess your readiness.

Request Your CRA Readiness Check.  

It's non binding and free of charge

Modern Development Allows for Easy 3rd Party Dependency Growth

The CRA Makes You Liable for All Your Software Components

The CRA makes governing 3rd parties your responsibility. The more components you have from different vendors, the more dependencies you must manage between them. If your stack contains a lot of open source or AI-generated code, all their potential hidden vulnerabilities are your responsibility. 

How do you ensure your product is updateable and patchable – throughout its lifecycle?


TIME IS RUNNING OUT

If you start now, you're already too late.

But we can help.

Lower Risks

Choose a stable and mature framework to cover more in one, instead managing various vendors or open source.

Lighter Burden

Stop using excess resources to keep your product secure throughout the years, also for 3rd-party components.

Ready-Made Parts

Reduce your efforts for secure features, documentation, and assessments, using ready-made building blocks.

Secure-by-Design Software

Design, develop and produce products securely, easily meeting technical feature requirements.

Vulnerability Management

Lower your risks significantly for your UI and middleware, including 3rd party components.

Reduced AI-Related Risks

Build on a solid product foundation, keeping agentic code a separate, manageable layer on top.

Long Lifecycles

Establish support throughout the product lifecycle easier, also beyond the minimum required 5 years.

Is Your Tech Stack Too Complicated?

The software components you bring in often come with dependencies to other components. As they bring along a significant maintenance burden, it is worthwhile to consider whether you need them all, or whether an entity that readily integrates several needed modules would serve you better.


Do You Need All Your Dependencies?

The CRA makes you liable for all of your technology stack, including all your 3rd party components and the dependencies that come with them.
Qt-SoftwareStackDependencies-SeparateComponents-1200-628

The more components you have from different vendors, the more dependencies you add to for you to manage and take the responsibility of. With fast-paced software creation, further boosted with agentic development, the number of dependencies grows incredibly fast. Especially with long product lifecycles, it builds up to what can be a very expensive and risky entity to maintain.

Do you know what you have in your stack?

Can you really manage it all, throughout the years?


Or Could You Consolidate?

For you as a product manufacturer, reaching and remaining CRA compliant becomes significantly easier with a certified framework from an experienced partner.
Qt-SoftwareStackDependencies-EntityofIntegratedModules-1200-628

Qt provides a single framework and integrated tooling to cover your needs from UI technology to core functionality, including internet protocols, networking, and connectivity. For all this, you get ready-made building blocks, topped with SBOMs, vulnerability management, threat and risk analysis, and technical documentation for Qt's part of your product.

A stable entity with a wealth of components

Commitment also for Qt's 3rd-party components


EXPERIENCED PLAYER IN REGULATED INDUSTRIES

Qt Is Your Trustworthy Partner for CRA Compliance

Thanks to the decades of history, with Qt, you have a very low risk. You also have a significantly reduced burden and effort to get and remain compliant, even for very long product lifecycles.

Meeting the strict security requirements of the CRA  is often practically impossible using only  open source software.

From our customers on switching from open source to Qt Commercial

How Qt 6.12 Makes Your CRA Compliance Easier

 Qt 6.12 is built to meet the requirements set by the CRA as we today know will take effect in December 2027, and Qt Group has officially completed the Conformity Assessment process for the commercial LTS release. As the regulatory standards are still evolving, the CE mark will be affixed as soon as there is further implementation guidance from the authorities. In the meantime, the signed Declaration of Conformity demonstrates Qt 6.12 CRA compliance, and we continue to ensure the conformity in the coming maintenance releases throughout the 5-year LTS support period.

Here, we’ve gathered a short summary of the tangible assets you get with the CRA-compliant Qt release.

SEE ALSO:
What Qt 6.12 CRA Compliance Means for You

Security by Design

 Qt Group's Quality Management System has been adapted for CRA compliance. In addition, Qt is ISO9001- and ISO27001-certified.

Qt Framework in general provides your development teams with building blocks for easier development of CRA-compliant & required features, and with the Qt 6.12 Commercial licenses, you can easily ensure compliance for Qt's part of your product.

In addition, compliance-considerations are a part of the daily Qt Framework feature development work. For instance, in Qt’s source code files, security critical items are marked according to the QUIP-23 process. 

Risk Management

 Qt Group has revised its risk management to meet the CRA requirements. The Threat Analysis & Risk Assessment is carried out whenever there’s a significant change, such as a new module or major feature, or an impactful architecture change. Each identified risk is scored for severity and likelihood, then assigned with a clear owner and tracked. The assessments are revisited whenever there are significant enough changes in the Qt libraries or APIS, whenever the threat landscape shifts, or when a new vulnerability surfaces.

Security by Default

 In general, the Qt API is of high quality; it is easy to use, and hard to misuse. In addition, the Qt Shared Security Model defines how the security responsibilities are divided between your team, the Qt Group, and the Qt Project.

As for meeting CRA’s technical feature requirements in your product, such as adding functionality for verifications, authentications, and more, Qt Framework provides various ready-made building blocks.

Vulnerability Management

 You have a very low risk for Qt’s part of your product.

Qt Group provides guaranteed response times (SLAs) to its commercial customers.

Qt Group has the official CNA status and we publish security advisories following our processes. Commercial customers can also sign up for the Early Warning List (EWL) to be the first to hear of found security issues. For developers, the issue tracking in the Jira bug tracker provides transparency.

Qt Framework is also committed to ensuring that for the used 3rd parties, the latest libraries are always integrated in the maintained Qt releases, lowering your risk further and easing your 3rd party management.

Security Maintenance

The commercial Qt 6.12 LTS release significantly helps in ensuring your products are updateable and patchable throughout their lifecycle, even for very long product lifecycles.

Qt LTS releases allow keeping your product in production in a stable and maintained environment. Security maintenance and updates are straightforward within the 5-year support period, and when needed, you can extend that with the Extended Security Maintenance (ESM) subscription or expand it with Extended Support​ and Professional Services.

This enables maintaining proprietary software without excess use of your internal resources, which would be the case with open source alternatives. 

SBOM, Documentation & Assessments

 Qt 6.12 Commercial provides you peace of mind with a wealth of documentation and assessment work ready-made for Qt's part of your product.

Qt can natively auto-generate a Software Bill of Materials (SBOM) during the build process to help with your CRA-compliance, vulnerability scanning, and file integrity.

In addition, Qt Framework comes with a wealth of technical documentation ready-made, easing your compliance efforts.

Qt 6.12 has been formally assessed against the CRA requirements, following Qt Group's Conformity Assessment process. The EU Declaration of Conformity for 6.12 LTS demonstrates the compliance.

EASE THE BURDEN

Security Maintenance Becomes a Significant Workload over the Years

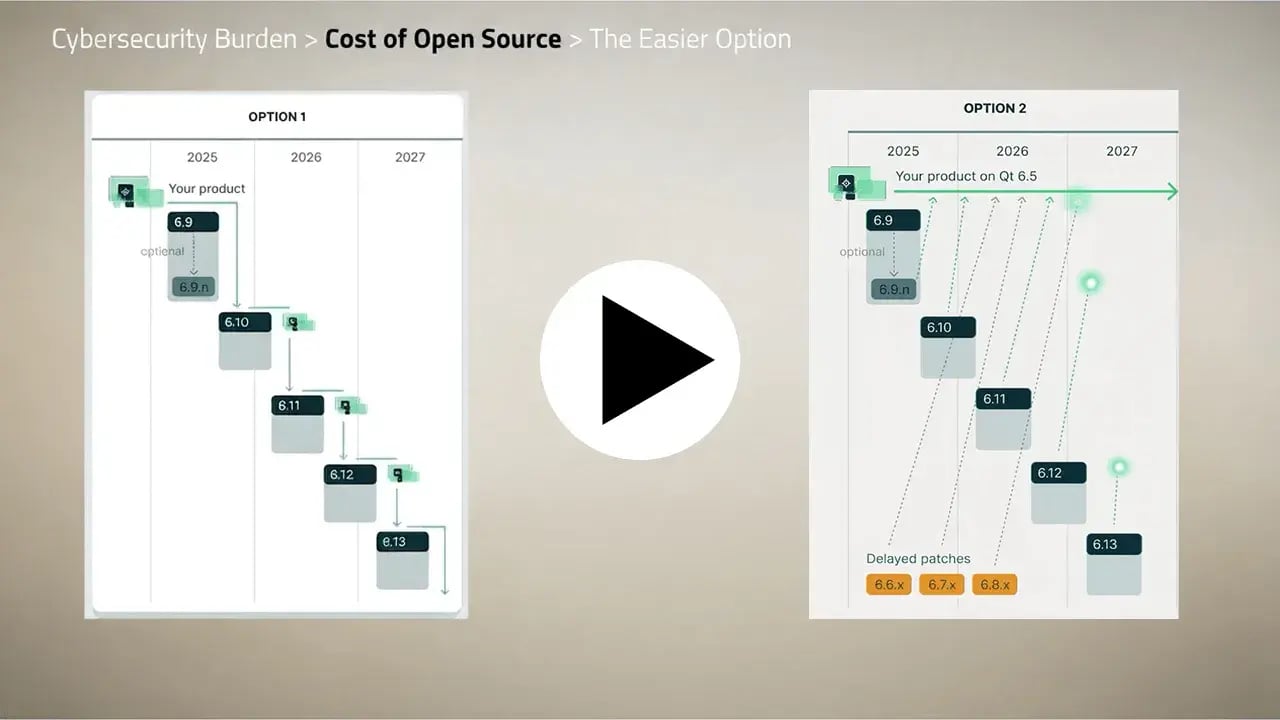
The commercial Qt LTS releases allow you to keep your product in production in a stable and maintained environment.

  • Overlapping 5-year-cycles allow updating in an organized manner.

  • You get all the maintenance and security patches immediately at their release.

  • You get first-hand information on the Early Warning List.

  • You can expand and extend the 5-year support with additional services.

The commercial licensing makes maintenance significantly easier.

The open source alternative leaves you with a significant maintenance burden to handle manually; either you update to every minor release every ~6 months, or you manually apply every single update and patch which you will only have access to with a delay. That will be a major workload and put you at serious risk of vulnerabilities in your product, which, in turn, puts you at a risk of CRA incompliance fines.

qt_foundation

WHAT IF YOU'RE NOT READY TO UPGRADE IMMEDIATELY?

A Temporary Option: Critical Security Patches for Legacy Releases

If you can’t upgrade from an older Qt Framework release after its end-of-support, you can extend your ability to maintain your product with the Extended Security Maintenance (ESM) subscription.

The ESM is a temporary solution that helps with compliance in a legacy Qt release while you’re updating to the newest LTS. ESM gets you access to security patches and you can combine it extended support for further assistance.

NEXT STEPS

You Need Cyber Resilience Act Compliance Now

A common misconception is that the CRA is a problem to worry about later in 2027.

The time is now.

The reporting requirements apply already from September 11th, 2026, and they apply retroactively also to products already on the market.

Request Your CRA Readiness Check

Our experts will help you identify the status of your technology stack, your processes such as vulnerability management and risk assessment, and your documentation, giving suggestions on the next steps.

Choose Your Path

Establish clear steps both in terms of your internal processes, managing your 3rd party components, as well as your potential needs for updating to the newest Qt release for easier Cyber Resilience Act compliance.

Meet Urgent Needs

If you’re not fully ready to upgrade to the newest Qt LTS release, assess your possibility to temporarily extend your security maintenance lifetime with the ESM and ES services for certain legacy Qt releases.

More on Qt Framework

Qt Framework’s comprehensive set of libraries take away your routines from middleware to UI, 2D to 3D, platform to platform.

More on the CRA

We've gathered the most important items from the regulation and their potential impact on you, into one concise webspace.

Get Started by Assessing Your Current Situation

Our experts can help identify your CRA readiness and help with next steps.